SSHole (CVE-2026-123158): Blue Team Detection & Response
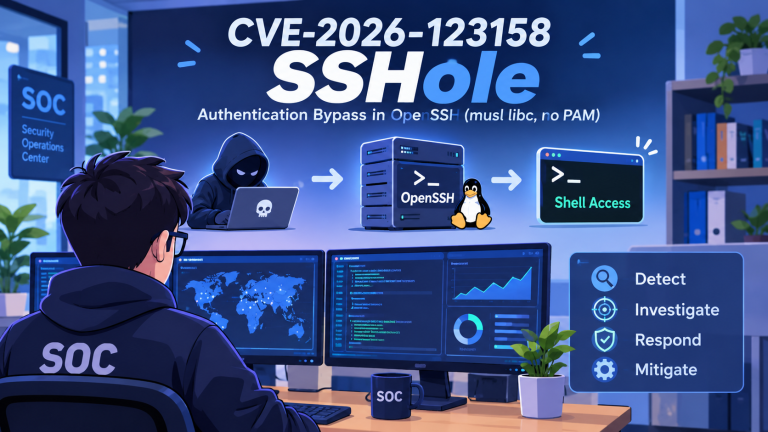
🔐 SSHole (CVE-2026-123158) – OpenSSH Authentication Bypass
Explored the Blue Team perspective of SSHole, a vulnerability affecting OpenSSH on Alpine Linux (musl libc without PAM).
The biggest detection challenge? Successful exploitation looks like a normal SSH password login.
🛡️ Key Blue Team Takeaways:
- Detect password logins on key-only accounts.
- Correlate failed and successful authentication attempts.
- Monitor suspicious post-login activity.
- Centralise SSH authentication logs.
- Patch OpenSSH and restart `sshd`.
Key lesson: Effective threat detection isn't always about finding malicious signatures. Sometimes, it's about identifying behaviour that should never happen.
#CyberSecurity #BlueTeam #ThreatHunting #DetectionEngineering #IncidentResponse #SSHole #OpenSSH #LinuxSecurity #SOC