SSHole (CVE-2026-123158): Blue Team Detection & Response
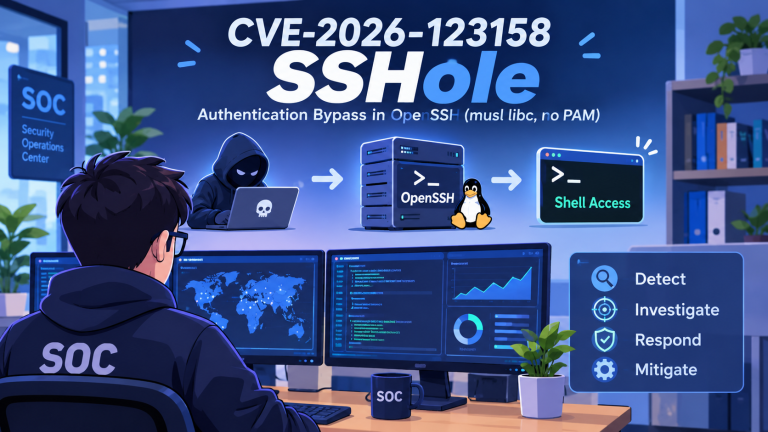
🔐 SSHole (CVE-2026-123158) – OpenSSH Authentication Bypass

Explored the Blue Team perspective of SSHole, a vulnerability affecting OpenSSH on Alpine Linux (musl libc without PAM).

The biggest detection challenge? Successful exploitation looks like a normal SSH password login.

🛡️ Key Blue Team Takeaways:

- Detect password logins on key-only accounts.
- Correlate failed and successful authentication attempts.
- Monitor suspicious post-login activity.
- Centralise SSH authentication logs.
- Patch OpenSSH and restart `sshd`.

Key lesson: Effective threat detection isn't always about finding malicious signatures. Sometimes, it's about identifying behaviour that should never happen.

#CyberSecurity #BlueTeam #ThreatHunting #DetectionEngineering #IncidentResponse #SSHole #OpenSSH #LinuxSecurity #SOC
SSHole: Alpine SSH Password Authentication Bypass

🔐 Exploring SSHole: OpenSSH Password Authentication Bypass

This material is provided for educational and research purposes only.

I explored SSHole, a vulnerability affecting OpenSSH password authentication on Alpine Linux systems, through hands-on lab testing and analysis.

The investigation focused on how oversized password inputs interact with musl libc and OpenSSH authentication logic, demonstrating how unexpected input handling can lead to authentication bypass.

This exercise provided valuable insights into SSH authentication mechanisms, Linux security, vulnerability analysis, and practical security testing.

#CyberSecurity #SSHole #OpenSSH #LinuxSecurity #AlpineLinux #VulnerabilityResearch #PenetrationTesting #Docker #InfoSec

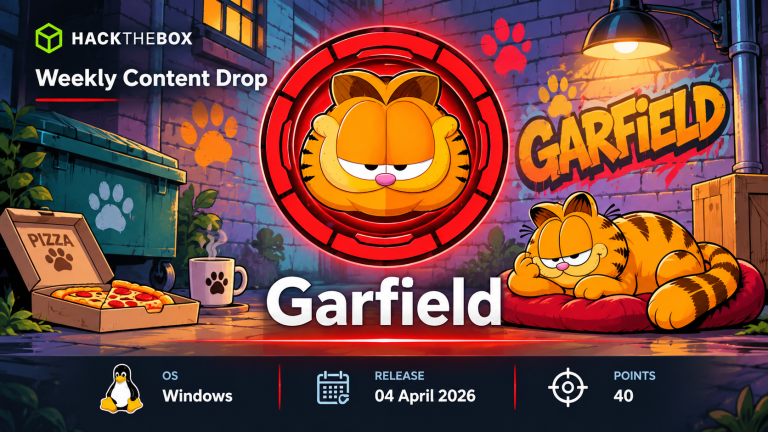
Hack The Box: Garfield Machine Walkthrough – Hard Difficulity

Just wrapped up the Hard-difficulty “Garfield” machine on Hack The Box which a really enjoyable Active Directory challenge.

The box starts with low-privilege domain credentials and requires solid enumeration to identify interesting attack paths. From there it moves into abusing writable attributes for initial code execution, pivoting through an internal network, and eventually targeting a read-only domain controller. The privilege escalation path involves computer account creation, resource-based constrained delegation, extraction of RODC-specific Kerberos material, and forging a golden ticket to achieve Domain Admin.

It was great practice for real-world AD red teaming techniques, especially around RODCs, Kerberos ticket manipulation, and modern delegation attacks. Highly recommend it if you’re looking to sharpen your Active Directory skills.

#HackTheBox #HTB #ActiveDirectory #RedTeam #CyberSecurity #PenetrationTesting #Kerberos #RODC #GoldenTicket #InfoSec

Hack The Box:MakeSense Machine Walkthrough Medium Difficulity

Completed MakeSense (Medium) from Hack The Box, achieving both user and root access.

The initial foothold involved investigating a custom WordPress theme and its voice transcription functionality. Source code analysis revealed a hard-coded encryption key and weaknesses in the application's AJAX implementation. Further investigation led to the recovery of administrator credentials, providing access to the WordPress dashboard. A malicious plugin then enabled remote code execution under the web server account. Additional enumeration uncovered credential reuse in the application configuration, allowing access to the local `walter` account and retrieval of the user flag.

The privilege escalation phase focused on an internally accessible OCR application running on port 8001. Process inspection revealed a root-owned service and script responsible for handling OCR operations. SSH port forwarding provided access to the internal application, where further investigation uncovered a weakness in its processing logic that allowed privileged command execution. The investigation also revealed a SUID-enabled Bash binary, providing an additional path to root access.

MakeSense provided valuable experience in WordPress security, JavaScript source code analysis, application-level vulnerabilities, Linux enumeration, and privilege escalation. It also highlighted how weaknesses in custom application functionality and internal services can lead to complete system compromise.

\#HackTheBox #HTB #MakeSense #WordPress #WebSecurity #LinuxPrivilegeEscalation #PenetrationTesting #OffensiveSecurity #RedTeam #CyberSecurity #EthicalHacking #LearningJourney

Dark Embargo — Technical Analysis of a PHP 8.4 Vulnerability

PHP2Shell: Investigating PHP 8.4 Memory Corruption Vulnerabilities

A technical exploration of PHP2Shell, focusing on CVE-2026-109618 and CVE-2026-109619, two vulnerabilities associated with PHP session upload progress handling and memory corruption.

The challenge provided an opportunity to examine PHP internals, investigate memory-management behaviour, and understand how these flaws could potentially lead to remote code execution.

The research also covered GDB-based debugging, Apache request handling, memory analysis, and the security implications of dangling session pointers.

Finally, the write-up examines PHP security updates and temporary mitigation measures, highlighting the importance of keeping PHP runtimes patched and properly configured.

#PHP #PHP2Shell #CVE #MemoryCorruption #CyberSecurity #VulnerabilityResearch #ApplicationSecurity #ExploitAnalysis #GDB #HackTheBox

Hack The Box: Checkpoint Machine Walkthrough Medium Difficulty

Just finished the Checkpoint machine on Hack The Box (Medium difficulty) and it was a really enjoyable Active Directory box with some modern and creative attack paths.

I started with the provided credentials for `alex.turner`. After some enumeration I discovered that a previously deleted account (`mark.davies`) could be restored and that this account had write access to a share called DevDrop. This share was used by the organisation to stage VS Code extensions.

By creating a malicious VSIX extension targeting VS Code engine version 1.118.0 and dropping it on the share, a scheduled task automatically installed the extension and gave me a reverse shell as `ryan.brooks`. This was a really clean example of abusing enterprise software deployment processes.

From the `ryan.brooks` foothold I used Rubeus to obtain a TGT, then leveraged bloodyAD to create a malicious dMSA under a writable OU and impersonated a higher-privileged account. This eventually granted access to a VMBackups share containing a Windows Server memory dump. Using Volatility I extracted the local Administrator NTLM hash from the dump, authenticated with Evil-WinRM, and captured the root flag.

Overall, Checkpoint does a great job of chaining together several current techniques: writable shares for extension abuse, deleted object restoration, dMSA abuse, and memory forensics. It’s a solid Medium box that feels realistic and rewards careful enumeration.

Would recommend it to anyone working on modern Windows / Active Directory attack paths.

#HackTheBox #CyberSecurity #PenetrationTesting #ActiveDirectory #RedTeam #HTB #InfoSec #WindowsSecurity #PrivilegeEscalation #Kerberos #MemoryForensics

Hack The Box: Eloquia Machine Walkthrough – Insane Difficulty

Just finished the Insane difficulty Eloquia machine on Hack The Box which one of the more layered and creative Windows boxes I’ve done in a while.

The path starts with a custom Django publishing platform that integrates with a Qoogle OAuth service. After registering and creating articles, you discover that the application trusts certain meta-refresh tags and can be leveraged for redirects. Combined with OAuth authorization flows and a bit of CSRF, this opens the door to higher-privilege access inside the web application.

From the admin interface, SQL Explorer becomes available. Because the backend is SQLite, `load_extension` can be abused to load a malicious DLL. That gives the first reverse shell as the `eloquia\web` user and the user flag.

Privilege escalation requires deeper enumeration. Edge browser credentials stored for the Olivia.KAT account can be extracted and decrypted offline. WinRM then provides a stable shell as that user. From there, Seatbelt and process enumeration reveal an interesting custom service called Failure2Ban that runs with high privileges and periodically restarts. By racing a binary overwrite of `Failure2Ban.exe` with a reverse shell, you land as `NT AUTHORITY\SYSTEM` and grab the root flag.

What made this machine feel genuinely Insane was the number of different skill sets required: web application logic, OAuth/CSRF, SQLite extension loading, Windows credential dumping, service abuse under AppLocker and PowerShell restrictions, and careful timing for the final binary overwrite.

Great learning experience overall.

#HackTheBox #CTF #PenetrationTesting #WindowsPrivilegeEscalation #RedTeam #InfoSec #Eloquia #InsaneBox

Hack The Box: Devhub Machine Walkthrough – Medium Difficulty

Completed another Hack The Box machine: Devhub (Medium).

Devhub was a great exercise in exploring modern development tooling, service misconfigurations, and Linux privilege escalation. The journey began with web enumeration and identifying an exposed MCP Inspector service. Further investigation revealed a command injection vulnerability that provided initial access to the machine.

From there, internal service enumeration uncovered a localhost-only Jupyter instance. Accessing it through SSH port forwarding and investigating its authentication mechanism opened the path to another user. The final stage involved examining an internal operations service, understanding its exposed functionality, and identifying a weakness that ultimately led to root access.

Devhub highlights how development tools, internal services, and poorly secured administrative functionality can create unexpected attack paths when combined. Another valuable machine for practising enumeration, lateral movement between local users, and privilege escalation.

#HackTheBox #HTB #CyberSecurity #PenetrationTesting #RedTeam #OffensiveSecurity #Linux #PrivilegeEscalation #WebSecurity #MCP #InfoSec

Hack The Box: Reactor Machine Walkthrough – Easy Difficulty

Completed another Hack The Box machine: Reactor, an Easy-difficulty Linux challenge.

The initial foothold came from enumerating the Next.js application running on port 3000. Version fingerprinting identified a vulnerable React canary release associated with CVE-2025-55182 (React2Shell). Further testing confirmed remote code execution through the React Server Components functionality, providing access as the node user.

From the application environment, the SQLite database exposed credentials for the engineer account. After recovering the password from the stored MD5 hash, SSH access provided the user-level foothold.

For privilege escalation, process enumeration revealed a root-owned Node.js service with the inspector exposed on localhost. The Node inspector provided a path to execute code within the root process and modify /bin/bash permissions, ultimately leading to a root shell.

I also explored an alternative approach using SSH local port forwarding and Chrome DevTools to access the remote Node inspector.

Another useful HTB machine for practicing web enumeration, version fingerprinting, application-layer exploitation, Linux enumeration, and Node.js debugging interfaces.

#HackTheBox #HTB #CyberSecurity #PenetrationTesting #RedTeam #OffensiveSecurity #WebSecurity #Linux #NextJS #React #NodeJS #CVE #PrivilegeEscalation #CTF #CyberSecurityLearning

Hack The Box: Smarthire Machine Walkthrough – Medium Difficulity

Completed another Hack The Box machine, SmartHire, rated Medium difficulty.

The attack path started with the SmartHIRE web application and its MLflow integration. Enumeration of the application exposed a vulnerable model workflow that allowed a reverse shell as the low-privileged svcweb user. After gaining access to the host, further enumeration revealed opportunities for privilege escalation.

The escalation path focused on the MLflow control script, which allowed malicious plugin code to execute with root privileges. This ultimately enabled the creation of a SUID Bash binary and provided a root shell. The final step was reading /root/root.txt to retrieve the root flag.

This machine provided a practical look at attacking MLflow-based applications, moving from web application exploitation to Linux privilege escalation, and chaining multiple weaknesses to achieve full system access.

#HackTheBox #HTB #CyberSecurity #PenetrationTesting #WebSecurity #Linux #MLflow #PrivilegeEscalation #OffensiveSecurity #RedTeam #EthicalHacking #InfoSec #CyberSecurityLearning #CTF #HTBWriteup