Category Hard Machine

Hack The Box: Garfield Machine Walkthrough – Hard Difficulity

Just wrapped up the Hard-difficulty “Garfield” machine on Hack The Box which a really enjoyable Active Directory challenge.

The box starts with low-privilege domain credentials and requires solid enumeration to identify interesting attack paths. From there it moves into abusing writable attributes for initial code execution, pivoting through an internal network, and eventually targeting a read-only domain controller. The privilege escalation path involves computer account creation, resource-based constrained delegation, extraction of RODC-specific Kerberos material, and forging a golden ticket to achieve Domain Admin.

It was great practice for real-world AD red teaming techniques, especially around RODCs, Kerberos ticket manipulation, and modern delegation attacks. Highly recommend it if you’re looking to sharpen your Active Directory skills.

#HackTheBox #HTB #ActiveDirectory #RedTeam #CyberSecurity #PenetrationTesting #Kerberos #RODC #GoldenTicket #InfoSec

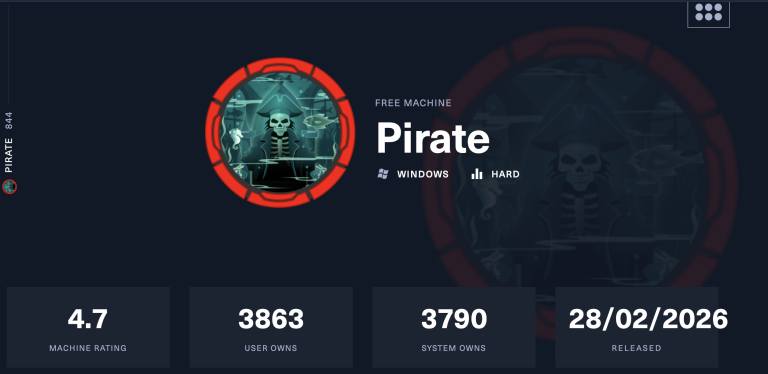
Hack The Box: Pirate Machine Walkthrough – Hard Difficulity

Completed the Hack The Box “Pirate” machine, a hard-difficulty Active Directory challenge that required chaining multiple attack paths rather than relying on a single vulnerability.

The enumeration phase uncovered domain users, pre-created computer accounts, GMSAs, delegation relationships, and an exposed internal network. Access to gMSA_ADFS_prod$ led to DC01 and enabled an internal pivot to WEB01. From there, the attack chain involved GMSA credential retrieval, NTLM relay, authentication coercion, shadow credentials, certificate-based authentication, and Kerberos ticket abuse.

The privilege escalation path continued through constrained delegation and resource-based constrained delegation. Kerberos ticket manipulation ultimately provided Administrator access to the domain controller, followed by a SYSTEM-level shell and extraction of domain credentials from NTDS.dit. Both the user and root flags were successfully obtained.

Another challenging AD machine completed and another deep dive into Windows authentication, delegation, and privilege escalation.

#HackTheBox #HTB #CyberSecurity #PenetrationTesting #ActiveDirectory #RedTeam #Kerberos #NTLMRelay #ShadowCredentials #GMSA #PrivilegeEscalation #WindowsSecurity #Cybersecurity #Infosec #HTBWriteup

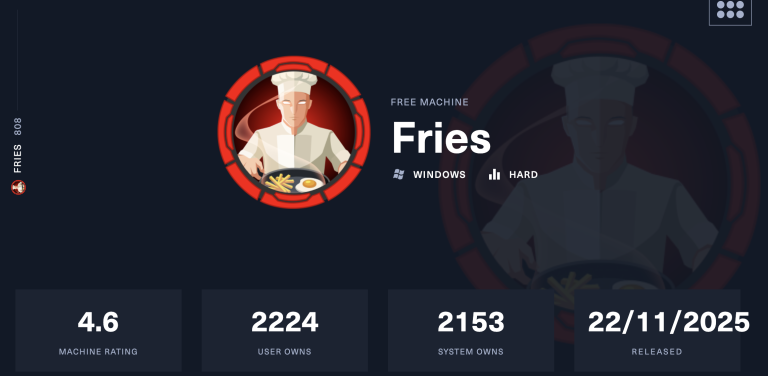
Hack The Box: Fries Machine Walkthrough – Hard Difficulty

Just wrapped up another Hack The Box machine: Fries (Hard).

TThis machine provided a realistic attack path that started with source code review in Gitea, where leaked credentials in a Git commit led to authenticated PostgreSQL RCE through pgAdmin. From there, I pivoted through the internal Docker network using Ligolo-ng, abused an exposed NFS share and debugfs to gain host access, then exploited PWM configuration weaknesses to capture LDAP credentials. The final stage involved Active Directory enumeration and AD CS (ESC6/ESC7) abuse to obtain an administrator certificate and compromise the domain. A great lab for practising web exploitation, Docker security, Linux privilege escalation, internal pivoting, and Active Directory attacks.

#HackTheBox #HTB #CyberSecurity #PenetrationTesting #RedTeam #ActiveDirectory #ADCS #Docker #Ligolo #PostgreSQL #Gitea #EthicalHacking #Writeup #CTF

Hack The Box: Nanocorp Machine Walkhtrough – Hard Difficulity

We completed the “Nanocorp” Active Directory lab on Hack The Box, covering full chain exploitation from initial access to domain compromise.

User access was achieved by exploiting a ZIP extraction flaw in a recruitment portal, leading to NTLM hash capture via a malicious .library-ms file and credential recovery for web_svc. Active Directory misconfigurations allowed privilege escalation to monitoring_svc through BloodHound-guided abuse of ForceChangePassword rights.

Root access was obtained after enumerating CheckMK Agent 2.1 on the Domain Controller. A web shell enabled command execution as web_svc, followed by exploitation of the CheckMK MSI repair process (CVE-2024-0670) using RunasCs to achieve SYSTEM-level access.

#HackTheBox #ActiveDirectory #Pentesting #RedTeam #PrivilegeEscalation #CyberSecurity #WindowsDomain #BloodHound

Hack The Box: Darkzero Machine – Hard Difficulity

Just completed the DarkZero machine from HackTheBox (Hard difficulty)!

After gaining a foothold on DC02 via a misconfigured MSSQL linked server and escalating to local Administrator using SigmaPotato token impersonation + RunasCs, we successfully captured the user flag from the Administrator’s desktop.

Dumped the domain Administrator NT hash with secretsdump, then used Evil-WinRM to get a full shell as Administrator on DC02 and retrieved the root flag.

#HackTheBox #HTB #Pentesting #ActiveDirectory #RedTeam #CyberSecurity #PrivilegeEscalation

Hack The Box: Guardian Machine Walkthrough – Hard Difficulty

🔐 User Flag — Compromising the Application Layer

Successfully rooted the Guardian (Hard) machine on Hack The Box by chaining multiple real-world web vulnerabilities.Initial access was achieved through credential abuse and IDOR within the student portal. Leaked chat credentials exposed internal Gitea repositories containing hardcoded database secrets. A vulnerable XLSX file upload feature allowed formula injection → XSS → session hijacking. Leveraging CSRF, I created a rogue admin account and escalated privileges within the application. From there, an LFI vulnerability combined with a PHP filter chain led to Remote Code Execution. After gaining a shell as www-data, I reused leaked credentials to pivot laterally to user jamil, capturing the user flag.

👑 Root Flag — From Code Injection to Full System Compromise

Privilege escalation started with sudo -l, revealing that jamil could execute a Python utility as user mark without a password. Since one of the Python files was writable, I injected code to spawn a shell as mark. Further enumeration uncovered a custom binary (safeapache2ctl) executable as root. A flawed validation mechanism in its Apache config parsing allowed path traversal and arbitrary file inclusion. By crafting a malicious shared object (evil.so) and abusing the wrapper’s improper include validation, I achieved root-level code execution and obtained a root shell.

Hack The Box: Mirage Machine Walkthrough – Hard Difficulity

Compromising the Mirage domain started with a simple clue hidden in an exposed NFS share. Inside a PDF report was a missing DNS record—just enough to pivot. By hijacking the DNS entry, I intercepted NATS JetStream traffic and captured real authentication logs, including valid credentials. After fixing the system time and obtaining a Kerberos TGT, I gained my first foothold on the domain controller and captured the user flag.

From there, the path to domain dominance unfolded through Active Directory weaknesses. An SPN ticket leak led to a cracked password, which opened the door to BloodHound reconnaissance and more credentials. I reset a disabled user’s password, extracted a service account’s managed password, and used Certipy to transform certificate abuse into full machine-level impersonation. With Resource-Based Constrained Delegation enabled, I forged Kerberos tickets, dumped every domain hash, and finally authenticated as Administrator—securing the root flag.

#CyberSecurity #PenetrationTesting #Kerberos #ActiveDirectory #RedTeam #HackTheBox #Infosec #PrivilegeEscalation

Hack The Box: RustyKey Machine Walkthrough – Hard Difficulity

Authenticated to rustykey.htb as bb.morgan after exploiting Kerberos flows and resolving a time sync issue: obtained a TGT (bb.morgan.ccache), set KRB5CCNAME, and used evil‑winrm to capture the user flag.
Escalated to SYSTEM by abusing machine account and delegation: IT‑COMPUTER3$ was used to modify AD protections and reset ee.reed’s password, S4U2Self/S4U2Proxy impersonation produced backupadmin.ccache, and Impacket was used to deploy a service payload to achieve a SYSTEM shell and capture the root flag.

#CyberSecurity #RedTeam #Kerberos #ActiveDirectory #PrivilegeEscalation #HackTheBox #Impacket #WindowsAD

Hack The Box: Certificate Machine Walkthrough – Hard Difficulty

I recently completed the "Certificate" challenge on Hack The Box: after extracting and cracking a captured authentication hash I gained access to a user account (lion.sk) and retrieved the user flag, then progressed to full system compromise by responsibly exploiting weak certificate‑based authentication controls—obtaining and converting certificate material into elevated credentials to capture the root flag. The exercise reinforced how misconfigurations in certificate services and poor time synchronization can create powerful escalation paths, and highlighted the importance of least‑privilege, strict enrollment policies, and monitoring certificate issuance. Great hands‑on reminder that defensive hygiene around PKI and identity services matters.

#CyberSecurity #HTB #Infosec #ADCS #Certificates #PrivilegeEscalation #RedTeam #Pentesting