Hack The Box: Eighteen Machine Walkthrough – Easy Difficulity
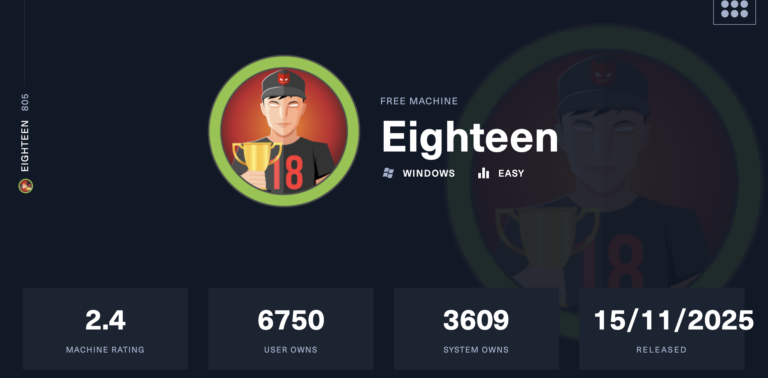
Just completed the Eighteen machine on Hack The Box — a great example of chaining multiple techniques from initial access to full domain compromise.
Gained initial foothold by cracking WinRM credentials (adam.scott / iloveyou1) and accessing the system via Evil-WinRM. From there, escalated privileges by abusing Delegated Managed Service Accounts (DMSA) using BadSuccessor, allowing impersonation of the Administrator.
Set up a Ligolo-ng tunnel to reach the domain controller, leveraged Kerberos ticket abuse with Impacket, and successfully dumped NTDS secrets. This led to extracting the Administrator NTLM hash and achieving full system compromise via Pass-the-Hash.
A solid walkthrough covering credential abuse, AD misconfigurations, Kerberos attacks, and pivoting techniques.
#HackTheBox #CyberSecurity #RedTeam #PenetrationTesting #ActiveDirectory #Kerberos #PrivilegeEscalation #EthicalHacking #Infosec #OffensiveSecurity