Tag ftp

Hack The Box: DevArea Machine Walkthrough – Medium Difficulty
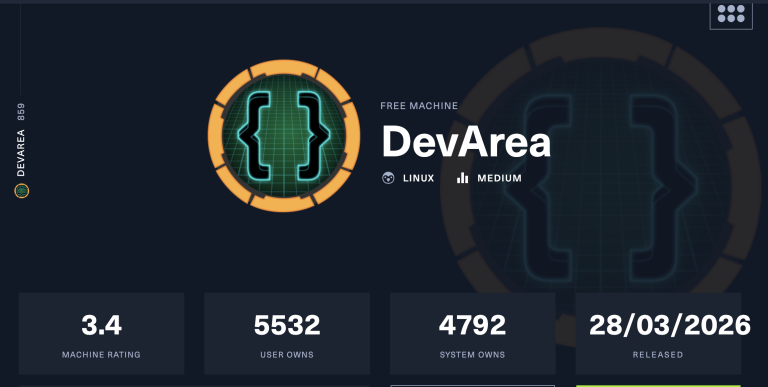
Just completed the DevArea machine from Hack The Box!

After exploiting a vulnerable Java SOAP service on port 8080, I gained initial access and discovered Hoverfly running on port 8888. Leveraging CVE-2025-54123, I successfully authenticated and delivered a reverse shell, securing the User flag as the dev_ryan user.

For privilege escalation, I took advantage of a sudo permission on the SysWatch management script. By exploiting a symlink attack in the logging functionality, I was able to read /root/root.txt and capture the Root flag.

Really enjoyed this Medium-difficulty box — great mix of Java deserialization/SOAP, API exploitation, and creative Linux privilege escalation!

#HackTheBox #HTB #PenetrationTesting #CyberSecurity #PrivilegeEscalation #CVE #EthicalHacking
Hack The Box: Era Machine Walkthrough – Medium Difficulity

Compromising the Era HTB machine involved chaining multiple weaknesses across the web layer and system layer. Initial access was obtained through an IDOR flaw in a file-sharing platform, allowing unrestricted file retrieval by enumerating numeric IDs. Leaked backups exposed source code, plaintext credentials, and an SSH private key, enabling lateral movement as eric. Further analysis uncovered a root-executed integrity-check binary in a world-writable directory. By extracting its signature, injecting it into a backdoored replacement, and waiting for the cron job to trigger, privileged execution was achieved. A resulting callback delivered full root access and allowed retrieval of the final flag.

#HTB #HackTheBox #CyberSecurity #Pentesting #WebSecurity #IDOR #PrivilegeEscalation #LinuxSecurity #RedTeam #CTF #InfoSec

Hack The Box: Administrator Walkthrough Medium Difficulty

Chained privilege escalation on an AD environment via misconfigured permissions — no CVEs, just clever abuse of default rights. From Olivia to Emily to Ethan, we pivoted through user relationships using BloodHound, CrackMapExec, Kerberoasting, and WinRM access. Highlighting how overlooked configurations can lead to full domain compromise.

#ActiveDirectory #PrivilegeEscalation #BloodHound #Kerberoasting #HackTheBox #RedTeam #CyberSecurity #WindowsPentest